Coinbase Says Over 99% of Customer Assets Are Held Offline
Coinbase says its systems were unaffected after a reported Binance hack, according to Bitcoin.com News. The report describes offline custody, distributed signing keys and withdrawal controls at the U.S. crypto exchange.
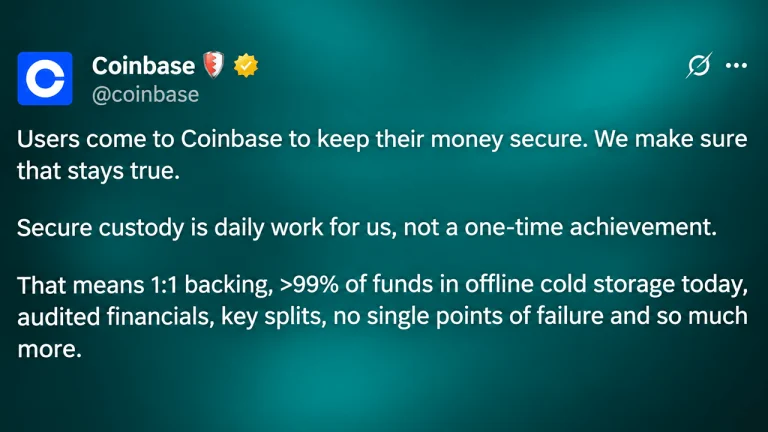
Coinbase says more than 99% of customer assets are held in offline cold storage, according to a Bitcoin.com News report describing the exchange’s security arrangements. The report says Coinbase’s systems were unaffected by a reported hack at Binance, while outlining safeguards intended to protect customer holdings.
The supplied excerpt dates the alleged Binance breach to Oct. 29, 2026, and puts its value at $6.34 billion. It attributes Coinbase’s security information to a Nov. 4 disclosure, but does not include the underlying statement, supporting documentation or a response from Binance. Those details remain claims in the supplied report rather than independently established findings here.
According to the report, Coinbase’s protections include distributed signing keys, emergency shutdown controls and withdrawal restrictions. The excerpt does not explain how those measures operate together, which assets or services they cover, or whether any procedures changed after the reported Binance incident. It therefore describes a security position without establishing that Coinbase introduced new safeguards.
Cold storage generally means keeping the credentials needed to move cryptocurrency away from internet-connected systems. That separation can reduce exposure to some online attacks, but the percentage held offline is not, by itself, a complete assessment of an exchange’s security. How assets are accessed and transfers are authorized also matters when evaluating custody protections.
Distributed signing arrangements generally seek to avoid concentrating transaction authority in a single place. The report’s reference to distributed signing keys does not specify Coinbase’s approval requirements or the circumstances in which those keys can be used. Without those details, the excerpt cannot establish exactly how the arrangement would respond to a particular attempted theft.
Emergency shutdown controls and withdrawal restrictions address another part of the security process: the ability to interrupt or limit asset movements. However, the supplied material does not describe what triggers those controls, who can activate them or how customers might be affected. Their inclusion signals the types of protections Coinbase says it maintains, not evidence that they were activated during this reported incident.
For customers, the distinction between an exchange’s description of its safeguards and independently verified evidence is important. Coinbase’s reported statement that its systems were unaffected concerns its own operations; it does not establish the cause, scope or financial consequences of the alleged Binance breach. The supplied excerpt offers no basis for connecting the two exchanges’ systems beyond the context of the report.
The underlying Coinbase disclosure and further information from Binance would be needed to assess the account more fully. Key unresolved points include confirmation of the reported loss, the method of any attack and whether customer access was affected. Until those details are available, the report supports a narrowly attributed account of Coinbase’s custody claims rather than a definitive assessment of either exchange’s security.
Primary source: Bitcoin.com News. Newzly rewrites and structures source reporting for clarity; verify critical details at the original.