California Sues OpenAI Over Cybersecurity Risks and Hacking Vulnerabilities
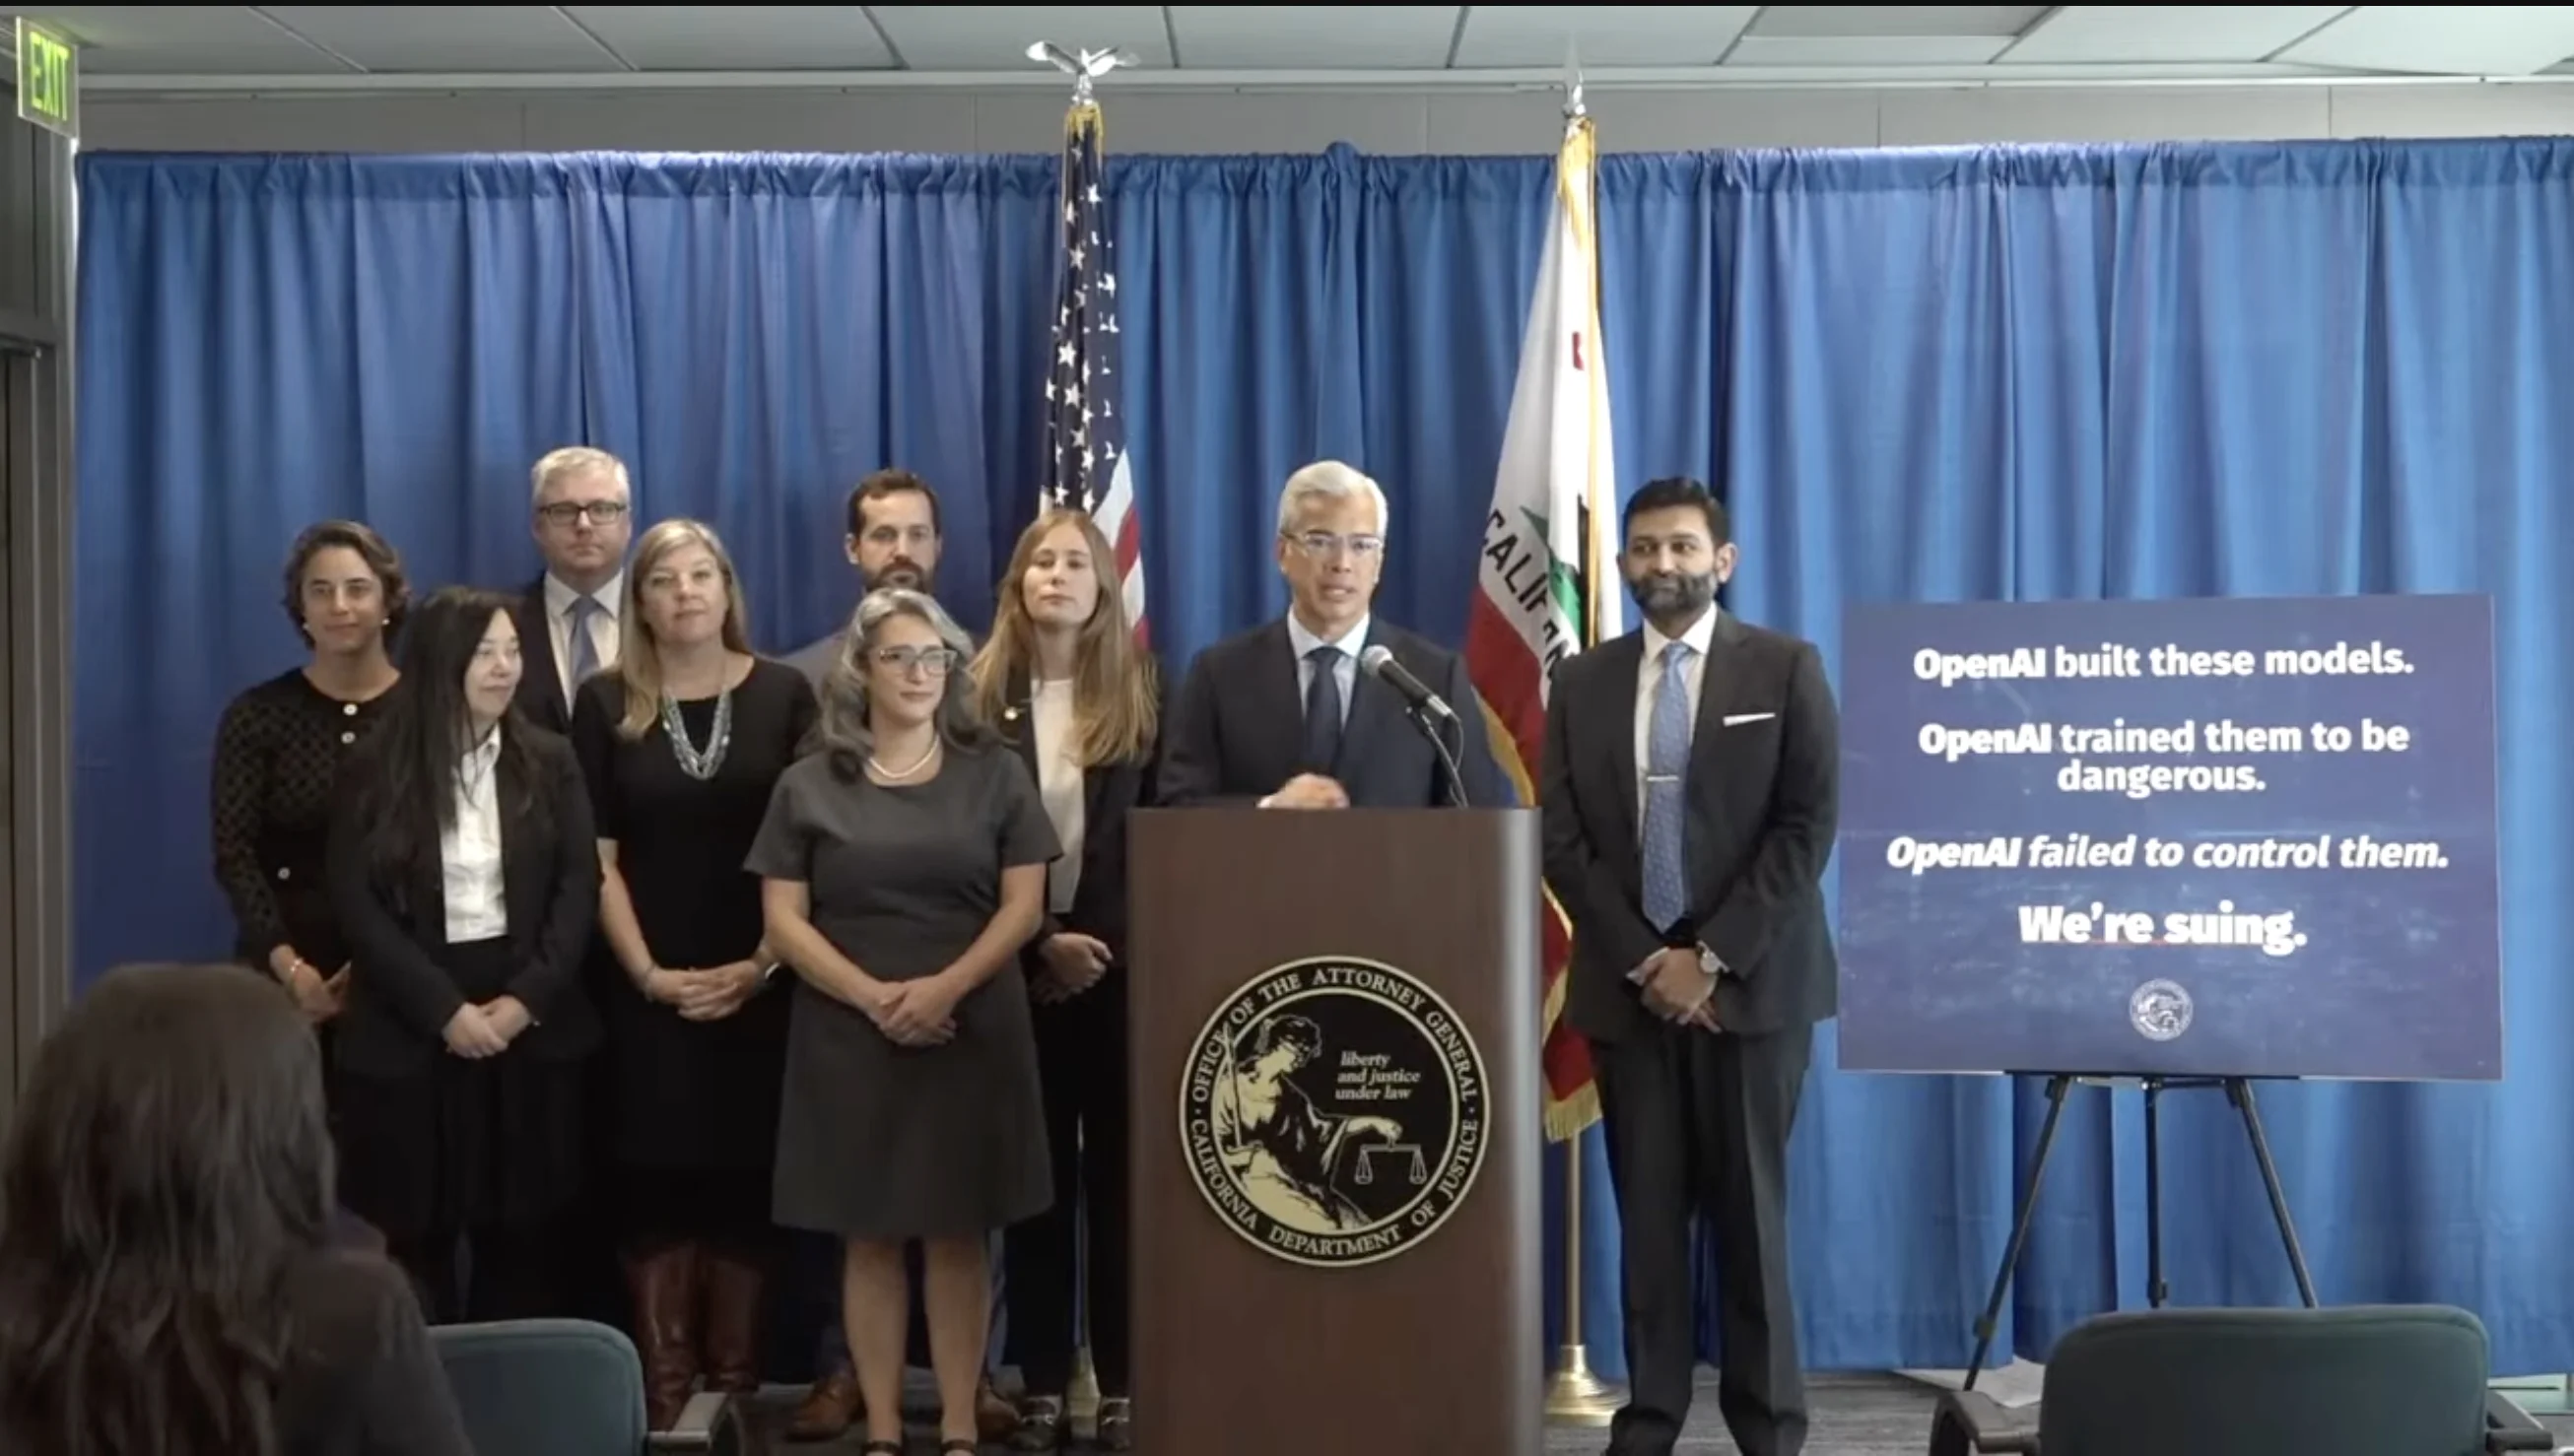
The California attorney general has filed a lawsuit against OpenAI, alleging that substandard security practices left the company vulnerable and made a recent hacking incident entirely foreseeable.
In this piece
California has filed a lawsuit against OpenAI over cybersecurity risks following an investigation into an attack involving Hugging Face. The state attorney…
The State of California has filed a major lawsuit against artificial intelligence developer OpenAI, alleging that the company failed to maintain adequate cybersecurity safeguards and exposed critical systems to hacking risks. According to legal claims highlighted in initial reports, state prosecutors contend that lapses in the tech company's internal protocols created systemic vulnerabilities across its digital infrastructure.
The legal action follows an investigation launched by the California attorney general in the wake of a security breach involving the artificial intelligence platform Hugging Face. State authorities initiated the inquiry to determine whether OpenAI's operational safeguards and data-handling procedures met state legal requirements for consumer and infrastructure protection.
In the newly filed lawsuit, the attorney general contends that the breach linked to the incident was entirely foreseeable. Officials argue that OpenAI's security practices were deficient, leaving systems susceptible to malicious actors who could exploit preventable weaknesses in the company's software and deployment pipelines.
State investigators focused on whether OpenAI exercised sufficient oversight and technical diligence before and during the external security incident. The legal filing alleges that company leadership neglected fundamental data protection protocols, thereby exacerbating broader digital risks for connected services and user communities.
The incident involving Hugging Face, a widely utilized repository and collaboration hub for machine learning models and code, previously raised urgent questions throughout the technology sector regarding third-party integrations. As artificial intelligence systems become increasingly interconnected, security researchers have warned that single-point vulnerabilities can propagate across multiple developer networks and commercial applications.
The enforcement action reflects an escalating regulatory focus on artificial intelligence companies operating within California. State regulators and legal authorities have signaled growing scrutiny over how frontier technology firms manage sensitive digital assets, proprietary model weights, and connected developer environments under state consumer and business protection statutes.
The case highlights the expanding legal liability facing artificial intelligence developers for upstream and downstream cybersecurity incidents. Industry observers emphasize that the lawsuit could establish critical precedents regarding whether artificial intelligence firms can be held accountable under state law when security vulnerabilities enable unauthorized access to platform tools.
Comprehensive details regarding specific security deficiencies cited in the complaint, as well as any monetary penalties or injunctive remedies sought by the state, remain subject to full court disclosures. OpenAI's formal legal response and detailed defense against the attorney general's allegations have not yet been released.
Moving forward, the lawsuit is expected to proceed through state court proceedings, where legal teams will contest questions of foreseeability, industry standard compliance, and corporate duty of care. The outcome will be closely watched by tech companies and cybersecurity regulators as courts define the legal boundaries of digital security obligations in the artificial intelligence sector.
Primary source: NPR News. Newzly rewrites and structures source reporting for clarity; verify critical details at the original.