LNbits Urges Immediate Server Shutdown Following Security Compromises
LNbits developers issued an urgent directive Sunday instructing node operators to take servers offline immediately after multiple active security exploits were reported across the Lightning Network platform.
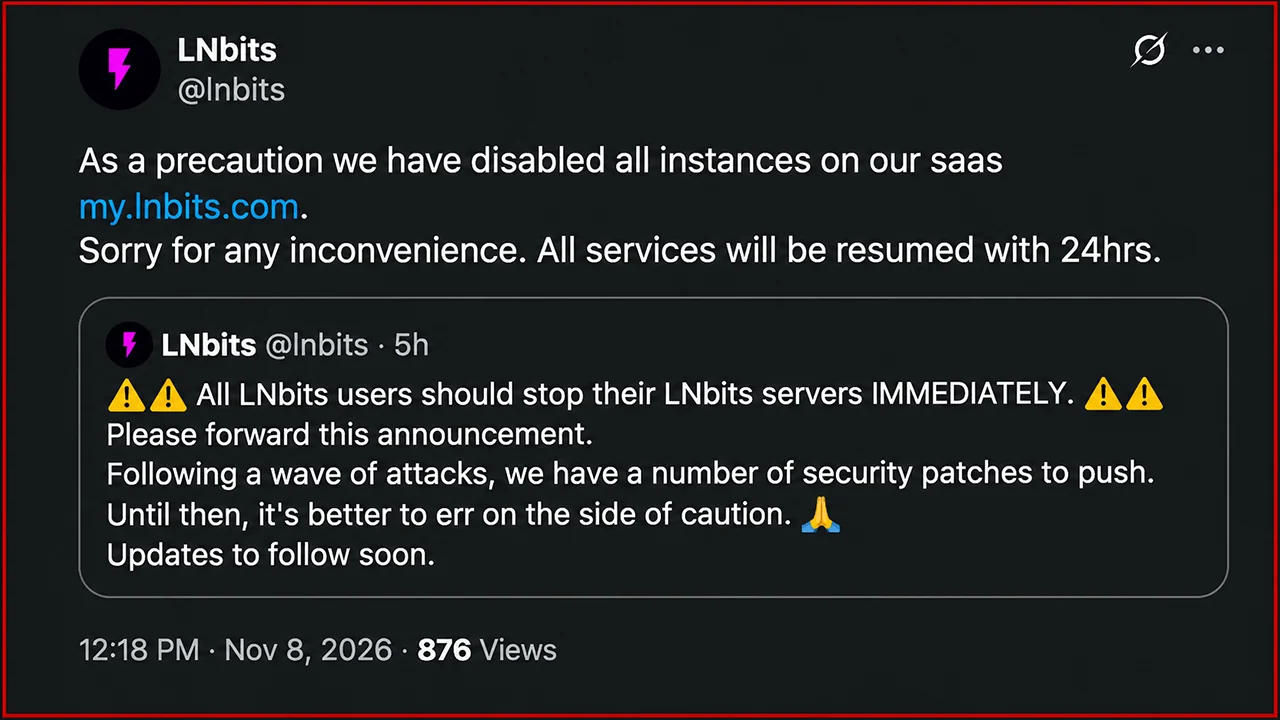
LNbits, an open-source Bitcoin Lightning Network wallet and payments platform, urged system administrators and node runners to shut down their servers immediately on Sunday, Nov. 8, 2026, following reports of multiple security compromises. The emergency directive came as project maintainers scrambled to identify and contain active exploits targeting running installations.
Developers instructed operators across both public-facing and private setups to sever active connections without delay to safeguard systems and connected nodes. The advisory emphasized that instances must remain completely powered down while engineering teams work against the clock to assemble and verify critical security patches.
LNbits serves as a popular modular software suite that functions as a lightweight accounting engine and application platform layered over Bitcoin's Lightning Network. By allowing operators to generate sub-wallets, configure point-of-sale systems, and run custom transactional extensions, the platform has become a foundational tool for independent merchants and community banks.
Because Lightning Network nodes maintain funded payment channels to facilitate instantaneous Bitcoin settlements, management platforms like LNbits interact directly with active capital. Any breach or unauthorized access at the software layer creates severe operational risks, potentially compromising backend keys, channel controls, or stored balances.
Initial reports from project maintainers and industry reporting did not disclose the precise technical exploit or specify whether the vulnerability originated in core application code or optional plugin extensions. The notification explicitly cited multiple unfolding attacks, pointing to an active threat environment rather than an isolated or theoretical proof-of-concept flaw.
Across the broader cryptocurrency and Lightning ecosystem, node operators and community service providers responded swiftly by taking instances offline and relaying the shutdown notice. Technical forums and developer chatrooms saw widespread coordination as administrators verified that their server daemon processes were halted and backend access tokens revoked.
The unfolding situation illustrates the complex operational trade-offs inherent in self-hosted financial technology. While decentralized and open-source payment software eliminates reliance on centralized custodians, it also leaves individual operators responsible for real-time incident containment and infrastructure security when critical bugs emerge.
Software maintainers are currently finalizing dedicated patches intended to close the security holes and protect affected server environments. Project contributors noted that detailed installation instructions, updated package builds, and configuration advisories will be published as soon as the remediation code has undergone preliminary validation.
For the immediate future, administrators are urged to keep all LNbits services strictly offline and avoid attempting partial mitigations until official releases are deployed. The community now awaits an in-depth post-mortem from the core team to clarify the exact scope of the compromise and outline hardening measures for future deployments.
Primary source: Bitcoin.com News. Newzly rewrites and structures source reporting for clarity; verify critical details at the original.