Cyber-Attack on European Supermarket Fridges Exposes Vulnerabilities in Connected Infrastructure
A cyber-attack targeting commercial refrigeration systems across European shops has forced store disruptions, spotlighting the growing cybersecurity risks facing internet-connected appliances and broader retail infrastructure.
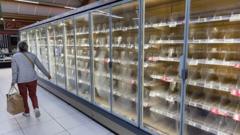
A cyber-attack targeting commercial refrigeration systems has disrupted operations across dozens of retail shops in several European nations, according to reporting from BBC Technology. The breach directly interfered with automated cooling units, forcing store managers to confront sudden operational disruptions. The unprecedented disruption has reignited critical questions surrounding the vulnerability of connected retail infrastructure.
While specific technical details regarding the perpetrators and point of entry have not been fully disclosed, the attack demonstrated that essential commercial appliances can be remotely manipulated. Grocers and convenience stores faced immediate hurdles in maintaining precise climate controls required for perishable goods. The incident prompted swift emergency evaluations across affected retail locations attempting to safeguard inventory and restore system stability.
The European store incidents illustrate how standard operational equipment has evolved into a potential target for digital saboteurs. Modern commercial refrigerators and freezers are rarely isolated appliances; instead, they frequently connect to local networks and cloud monitoring platforms to track temperature compliance, optimize energy usage, and automate maintenance diagnostics. This digital transition offers operational efficiency but expands the potential attack surface.
Security specialists have long cautioned that operational technology and Internet of Things devices often lag behind traditional enterprise IT systems in defensive hardening. Industrial controllers, digital thermostats, and connected cooling units frequently rely on lightweight firmware that may lack multi-factor authentication or robust patch management pipelines. Once an intruder gains access to these connected endpoints, lateral movement across corporate networks becomes an urgent concern.
The tangible risks of such intrusions extend far beyond digital inconvenience to immediate physical and financial damage. In the grocery sector, sudden temperature spikes can compromise massive volumes of chilled food, triggering mandatory health disposal regulations and substantial economic losses. Furthermore, unexpected equipment downtime disrupts customer service and strains local supply chains that depend on consistent product turnover.
The geographic spread across multiple European borders suggests the vulnerability may stem from shared third-party software, remote maintenance providers, or standardized industrial control systems. Many supermarket chains deploy uniform management platforms across international outlets to streamline centralized administration. When a single remote management interface or software provider is compromised, the fallout can quickly propagate through independent retail outlets across multiple jurisdictions.
The broader implications extend well beyond supermarket aisles to other sectors reliant on automated thermal controls and connected environmental hardware. Critical operations ranging from pharmaceutical storage and medical distribution centers to data centers and agricultural warehouses employ comparable connected infrastructure. Analysts observe that if basic commercial refrigeration can be subverted, similar vulnerabilities could threaten other temperature-critical supply chain links.
In the wake of the attacks, enterprise operators and regulatory bodies across Europe are expected to intensify oversight of connected commercial appliances and vendor access controls. IT teams will likely face heightened pressure to implement strict network segmentation, ensuring operational technology cannot be reached from open networks. As investigations proceed, the incident is poised to accelerate calls for mandatory security baselines for all internet-enabled commercial hardware.
Primary source: BBC Technology. Newzly rewrites and structures source reporting for clarity; verify critical details at the original.